CDWTCDWT

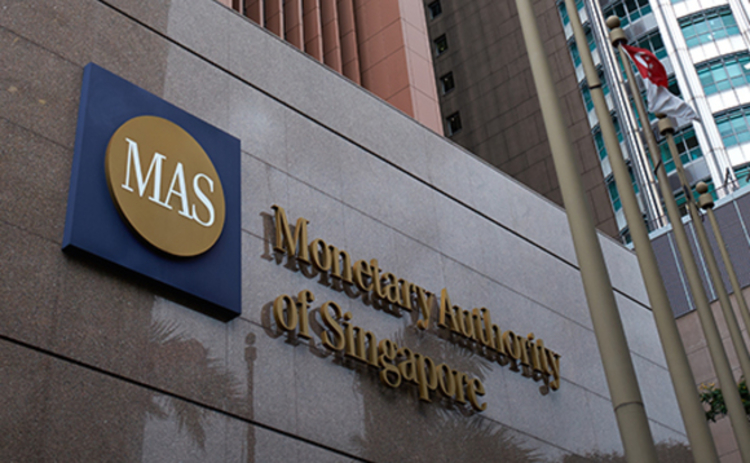
MAS – Monetary Authority Of Singapore – Compliance

Obtaining Full Data Integrity and Immunizing Organizations Against Cyberthreats with MAS Compliance Services that are fully managed.

CYBER-SECURITY

Maximize Security and the Shield for Future Growth Without Compromise

Today’s organizations handle more data than ever before, which necessitates a plethora of safeguarding duties. The effect is evident in the form of financial losses, increased operational expenses, performance hazards, compromised data security, management of conflicts of interest, and efficient customer service. As firms struggle to comply with data privacy and protection laws, regulatory compliance has become an arduous and arduous undertaking.

MAS is unquestionably the best method for implementing wider controls across IT security operations. It plays a crucial role in mandating frequent risk assessment, establishing and maintaining security policies, conducting regular security testing, managing software and patches, protecting against malware, and defending against sophisticated threats.

Enhancing Cybersecurity with MAS Compliance – Singapore’s Monetary Authority

MAS-COMPLIANCE-PNG
MAS COMPLIANCE
CDWT
Increase regulatory emphasis while bolstering public trust.
Why MAS Compliance is Required

ompliance with cybersecurity regulations is rising importance in technology-driven banking. Cyber resilience frameworks are urged to handle significant challenges such as data security and integrity, regulatory risks, reputational harm, etc. In the following ways, an inclusive and compliance-focused financial activity may benefit:

MAS Compliance Mapping

Phase 1: Planning and Assessment
  • During this phase, regulatory inspectors conduct face-to-face discussions and seminars to review the business environment, current architecture, procedures, and services of financial institutions.
  • Additionally, this individual discovers systems and infrastructures that fall within the scope of MAS TRM rules and technologies.
  •  
Phase 2: Adopt
  • This step involves analysing all current policies, procedures, and processes to establish the effectiveness with which financial institutions manage technological risk and cyber resilience.
  • The regulatory inspector employs and conducts sample-based testing to evaluate controls and ascertain the operational efficacy of the proposed and implemented system.
  •  
Phase 3: Review and Recommendation
  • During this step, the regulator inspector prepares reports based on the fieldwork results and delivers them to the organization.
  • It discusses the possible gaps observed in comparison to the MAS TRM Guidelines, as well as specific areas for improvement and appropriate recommendations for filling those gaps.
  •  

Managed Compliance Services from CDWT

CDWT’s Managed Compliance Services enable enterprises to supplement their IT infrastructure, security networks, cloud platforms, data structures, and software/apps in order to become completely compliant with global legislation and standards.

We investigate customer landscapes, access functionalities, and workloads in collaboration with A-star compliance professionals and modern technologies to validate whether or not they adhere to respective protocols while bestowing effective strategies and employing critical processes to risk-proof compliance globally. CDWT Managed Compliance Services protect essential cloud platforms including hyperscaler cloud landscapes, private clouds, third-party environments, on-premises or remote ecosystems, and assist them in becoming completely compliant with the following services:

MAS-COMPLIANCE-PNG
MAS COMPLIANCE
CDWT
Increase regulatory emphasis while bolstering public trust.
Why Partner with CDWT to Achieve Compliance in Your Industry?

The world's biggest Application-focused Managed Cloud Services Provider and a leader in managed cybersecurity. Dedicated security evaluation services.

12+ years of service to 4000+ corporations, including 60+ Fortune 500 companies, in 25+ countries spanning the Americas, Europe, Middle East, and APAC.

More than 40 Security Controls, twenty Centres of Excellence, and two thousand worldwide cloud specialists

Pre-met compliance demands for local, national, and international compliance regulations, such as IRAP, GDPR, HIPAA, SAMA, CSA, GXP, and ISO Certifications.

3200 UTMs, 13000 HBSS, 800000 EPS

Seven Security frameworks using the MITRE ATT&CK, CIS Critical Security Controls, and more

Comprehensive 24x7 monitoring of cyber security

Advanced Managed Detection and Response Solutions Automated Security Solutions for threat prediction, detection, and response (MDR)

Expertise in managed SOC (Security Operations Center) services and solutions on a global scale.

DevSecOps-specific portfolio

Cybersecurity Consulting, Cybersecurity Assessment, and Audit Reporting Services for the Entire IT Stack and Cloud Infrastructure.

Advanced Cybersecurity Incident and Response Team (CSIRT) for CDWT

Threat Intelligence powered by Industry-leading platforms such as Microsoft, OSINT, STIX&TAXI, MISP, etc. and CDWT Threat experts

Considerable threat management knowledge in protecting big and complex settings and using the sophisticated features of industry-leading technologies and Cloud-Native Security products.

Expertise in building and administering comprehensive SIEM - assisting organisations in proactively assessing vulnerabilities and automating and accelerating incident response.