CDWTCDWT

Continuous Integration – Continuous Delivery (CI – CD) Security

Integrate enhanced security into the CI/CD pipelines of the enterprise. Enhance DevSecOps methods for optimum productivity and operational continuity

CYBER-SECURITY

Shielding the CI/CD Pipeline Is the First Step in Establishing a Successful DevSecOps Environment.


As a discipline and culture, DevSecOps has grabbed the IT industry by storm. IT security, operational, and development teams have operated autonomously for aeons, resulting in frequent goals conflicts that have finally caused delivery schedule delays. After multiple testing and iterations, software was often released to operate important systems, only to be denied by a security filter anticipating weaknesses in the codebase.

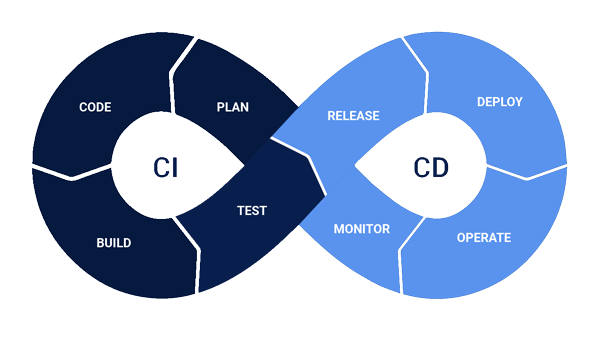
This prompted the development of updated application, software development, testing, and deployment environments that included security checks, frameworks, and tools at each operational stage. Modernized development environments are implemented using CI/CD (Continuous Integration/Continuous Delivery) pipelines, and the DevSecOps model of a company is driven by the security integration of these pipelines.
Why Continuous Integration and Continuous Delivery (CI/CD) Security?

Advantages of Implementing Specialized CI/CD Security Services and Solutions

DATABASE-ACTIVITY-MONITORING-BANNER
CI/CD SECURITY
CDWT
Contact Our DevSecOps Professionals

Implementation Best Practices and Immediate Strategies for CI/CD Security

CDWT DevSecOps and CI/CD Security End-to-End Solutions and Services

DATABASE-ACTIVITY-MONITORING-BANNER
CI/CD SECURITY
CDWT
Contact Our DevSecOps Professionals

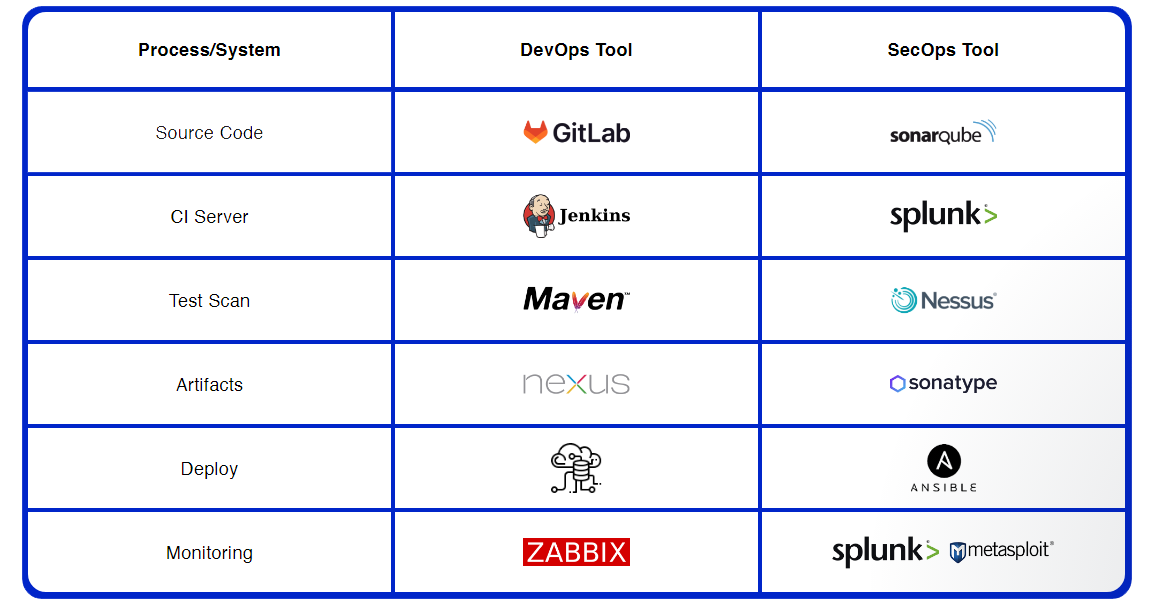
SecOps Solutions and Tools

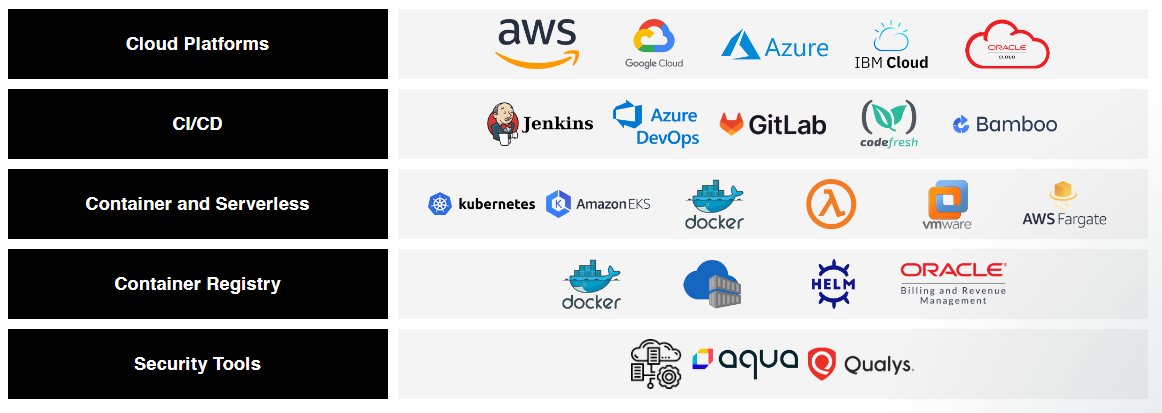
Cloud DevSecOps & CI – CD Landscape

What Makes CDWT’s DevSecOps and CI/CD Security Solutions and Services Unique?

The world's biggest Application-focused Managed Cloud Services Provider and a leader in managed cybersecurity. Dedicated security evaluation services.

12+ years of service to 4000+ corporations, including 60+ Fortune 500 companies, in 25+ countries spanning the Americas, Europe, Middle East, and APAC.

More than 40 Security Controls, twenty Centres of Excellence, and two thousand worldwide cloud specialists

Pre-met compliance demands for local, national, and international compliance regulations, such as IRAP, GDPR, HIPAA, SAMA, CSA, GXP, and ISO Certifications.

3200 UTMs, 13000 HBSS, 800000 EPS

Seven Security frameworks using the MITRE ATT&CK, CIS Critical Security Controls, and more

Comprehensive 24x7 monitoring of cyber security

Advanced Managed Detection and Response Solutions Automated Security Solutions for threat prediction, detection, and response (MDR)

Expertise in managed SOC (Security Operations Center) services and solutions on a global scale.

DevSecOps-specific portfolio

Cybersecurity Consulting, Cybersecurity Assessment, and Audit Reporting Services for the Entire IT Stack and Cloud Infrastructure.

Advanced Cybersecurity Incident and Response Team (CSIRT) for CDWT

Threat Intelligence powered by Industry-leading platforms such as Microsoft, OSINT, STIX&TAXI, MISP, etc. and CDWT Threat experts

Considerable threat management knowledge in protecting big and complex settings and using the sophisticated features of industry-leading technologies and Cloud-Native Security products.

Expertise in building and administering comprehensive SIEM - assisting organisations in proactively assessing vulnerabilities and automating and accelerating incident response.

Continuous Integration – Continuous Delivery (CI – CD) Security – FAQ’s

Continuous Integration and Continuous Delivery Pipelines (CI-CD Pipelines) are automated methods that enable to modernize and accelerate application development, testing, and deployment. CI/CD Security hence refers to the implementation of security solutions and procedures, such as vulnerability assessment, real-time threat monitoring, threat remediation, and key management.
CI/CD pipelines and procedures are often automation systems designed to accelerate the stages of software/application creation, testing, and deployment. Consequently, access is often granted to numerous libraries, source code files, key vaults, and secret information centres, among others. CI/CD Security solutions examine all such processes for weaknesses, such as unforeseen threats and pre-planned assaults. Monitoring systems examine pipelines 24 hours a day, seven days a week, and trigger immediate remedial procedures when malicious code, threats, or intrusions are found. In addition to bolstering the security of in-development apps and incorporating security-by-design, this activity entails enhancing their security.
Without requiring human involvement, CI/CD technologies, procedures, and pipelines such as Jenkins, GitLab, and Bamboo automate numerous application/software development, testing, and deployment operations. CI/CD pipelines have access to development environment access codes, platform IDs, keys, and authentications to complete the aforementioned duties efficiently, hence increasing the DevOps team's overall productivity.