Application Security Testing – AST Solutions and Services
Secure Software, runtime apps, codebases, builds, CI/CD pipelines, and avoid vulnerabilities using Mobile Application Security Testing, Static Application Security Testing (SAST), and Dynamic Application Security Testing (DAST)
Automate and Report on critical vulnerabilities across Enterprise Development Landscapes
The incredible increase in the use of mobile apps, online applications, and workplace apps to modernize everyday and business ‘lifestyles’ has provided cybercriminals with an unparalleled ‘fodder-verse’ According to reports, up to fifty percent of online applications include at least one significant vulnerability. In addition, the findings indicate that it takes IT teams between six and nine months to uncover such vulnerabilities and implement the necessary corrective measures.
On the basis of the foregoing timescales, it would be erroneous to suggest that IT people are insufficiently agile. In the majority of company settings, developer and maintenance teams outweigh security engineers and experts by a significant margin. Additionally, business owners prioritize product development, delivery, and market introductions above proper testing processes. Even in the case of major enterprises with gigantic cybersecurity teams, it is difficult to manually review millions of lines of code on a frequent basis in search of a single vulnerability. Therefore, the need for extra reinforcements in modernizing cybersecurity management in the core development environments cannot be minimized.
Enhance DevOps Security Knowledge with Interactive Application Security Testing
Application Security Testing (AST) is a collection of tools, solutions, protocols, software composition analysis solutions, and procedures that automate all security administration activities pertaining to app development, testing, and deployment, including CI/CD pipelines. AST solutions often evaluate applications and their backend codebases at an astounding rate, in the millions of lines per minute. Regardless of sector or specialty, investments in Application Security Solutions and AST have multiplied over the last few years.
Solutions for Static Application Security Testing (SAST)
Positive aspects of Static Application Security Testing (SAST Scan/Test).
Solutions for Dynamic Application Security Testing (DAST)
Positive aspects of Dynamic Application Security Testing (DAST Scan/Test).
A Comparison between Static Application Security Testing (SAST) & Dynamic Application Security Testing (DAST)
SAST
-
White Box Testing: SAST tools examine from the inside out all source code files, codebases, libraries, and CI/CD processes.
-
Works only while a programme is inactive; realtime software development is ineffective Lifecycle
-
Early detection of security vulnerabilities and threats in software development.
-
Because flaws are spotted in the source code at the code line level, they are less expensive to rectify.
-
Examines every programme at the source-code level.
-
In 90 days, a successful Internet-based B2B marketplace system was produced.
-
DAST
-
Black Box Testing: Deploys simulated assaults to infiltrate the application from the outside without integrating internal codebases.
-
Deployed when an application is in operation
-
Led a team of twelve resources, focusing on Siebel administration, automation of existing processes, concurrent development methods/strategies and resource management
-
Comparatively more costly since the vulnerability site must be further evaluated if problems are found.
-
Typically relevant exclusively to web applications
-
Independent of the language or fundamental platforms the application was developed on.
-
Interactive Application Security Testing Is the Foundation of a Prosperous DevSecOps Model
As a discipline and culture, DevSecOps has grabbed the IT industry by storm. IT security, operational, and development teams have operated autonomously for aeons, resulting in frequent goals conflicts that have finally caused delivery schedule delays. After multiple testing and iterations, software was often released to operate important systems, only to be denied by a security filter anticipating weaknesses in the codebase. This prompted the development of updated application, software development, testing, and deployment environments that included security checks, frameworks, and tools at each operational stage. The foundation of a company’s DevSecOps paradigm is driven by severe Application Security Testing solutions, such as SAST and DAST, applied to modernised development environments.
End-to-end CDWT DevSecOps and Application Security Testing (AST) Services and Solutions
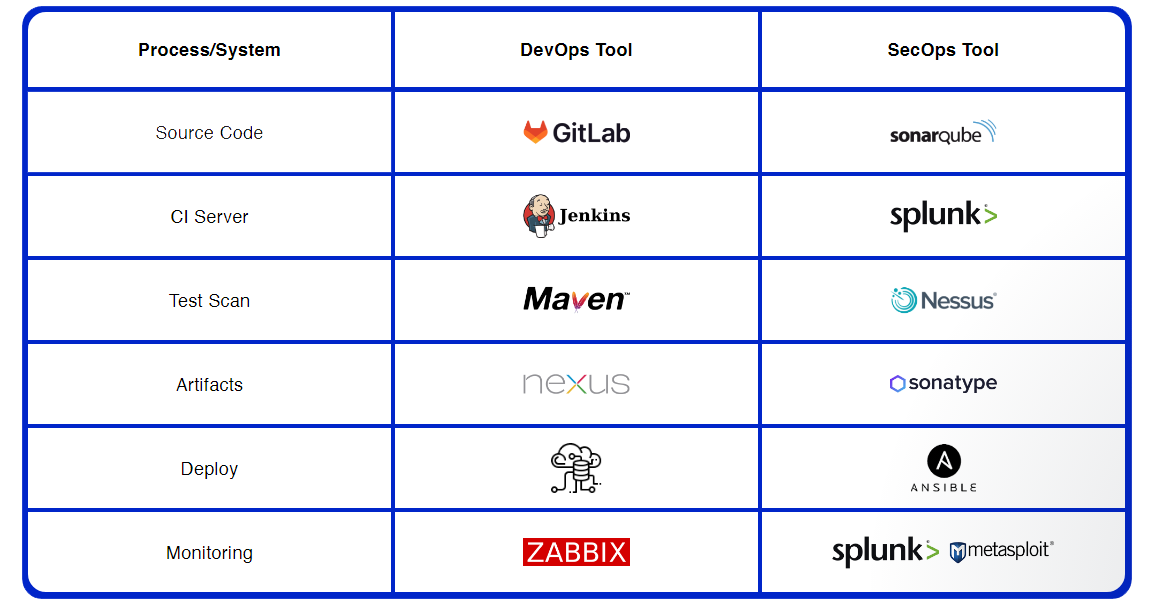
DevSecOps Solutions and Tools
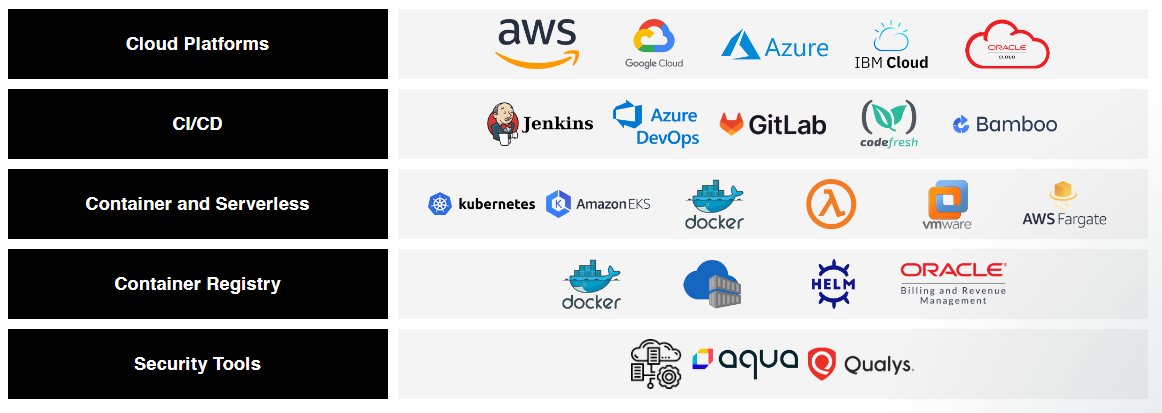
Cloud DevSecOps Landscape
What Makes CDWT’s DevSecOps Security Solutions and Services Unique?
The world's biggest Application-focused Managed Cloud Services Provider and a leader in managed cybersecurity. Dedicated security evaluation services.
12+ years of service to 4000+ corporations, including 60+ Fortune 500 companies, in 25+ countries spanning the Americas, Europe, Middle East, and APAC.
More than 40 Security Controls, twenty Centres of Excellence, and two thousand worldwide cloud specialists
Pre-met compliance demands for local, national, and international compliance regulations, such as IRAP, GDPR, HIPAA, SAMA, CSA, GXP, and ISO Certifications.
3200 UTMs, 13000 HBSS, 800000 EPS
Seven Security frameworks using the MITRE ATT&CK, CIS Critical Security Controls, and more
Comprehensive 24x7 monitoring of cyber security
Advanced Managed Detection and Response Solutions Automated Security Solutions for threat prediction, detection, and response (MDR)
Expertise in managed SOC (Security Operations Center) services and solutions on a global scale.
DevSecOps-specific portfolio
Cybersecurity Consulting, Cybersecurity Assessment, and Audit Reporting Services for the Entire IT Stack and Cloud Infrastructure.
Advanced Cybersecurity Incident and Response Team (CSIRT) for CDWT
Threat Intelligence powered by Industry-leading platforms such as Microsoft, OSINT, STIX&TAXI, MISP, etc. and CDWT Threat experts
Considerable threat management knowledge in protecting big and complex settings and using the sophisticated features of industry-leading technologies and Cloud-Native Security products.
Expertise in building and administering comprehensive SIEM - assisting organisations in proactively assessing vulnerabilities and automating and accelerating incident response.
Application Security Testing – AST – FAQ’s
That is, malicious assaults that may occur owing to code-based deficiencies. The benefit of SAST is that monitoring and audits are performed automatically throughout the development process, warning developers of any code-based restrictions that might compromise security. The thorough SAST reports include charts, graphs, and insights that highlight issues at the code level.